terça-feira, 9 de junho de 2020

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

How To Recover Files That Are Deleted From Recycle Bin

Well, Windows users have a bad habit of removing files from recycle bin. Deleting useless files from Recycle Bin helps a user to save some storage space which can improve the speed of a computer. However, Windows users do that more frequently and later regret. Actually, Recycle Bin is a place from where we can get back our deleted files and folders.
Sometimes, we accidentally delete our important files and folders and due to some reason we lose them from Recycle bin too! At that time, we search for recovery methods. Well, there are many methods available over the web which can help you to recover deleted files from computer, but, when it comes to reliability, nothing can beat EaseUS.

What Is EaseUS Data Recovery Wizard?
EaseUS is one of the leading software providers which is known for its data recovery programme. EaseUS offers some free data recovery software that can help you to recover deleted, formatted or lost data from PC, laptop or removable device easily and quickly.
One of the best thing about EaseUS is that it provides tools for recycle bin recovery which can help you to get back files that you have deleted from the Recycle bin itself. EaseUS Data Recovery Wizard free can easily recover lost files, pictures, documents, videos and more from deleting, formatting, partition loss, OS crash, virus attack and other data loss cases.

How To Recover Deleted Files?

If you are struggling to get back your lost data files, then here is an easy data recovery method which will help you to get back deleted files on your computer. Below, we are going to share a mini guide on how to use EaseUS Recycle Bin Recovery to get back your deleted data.
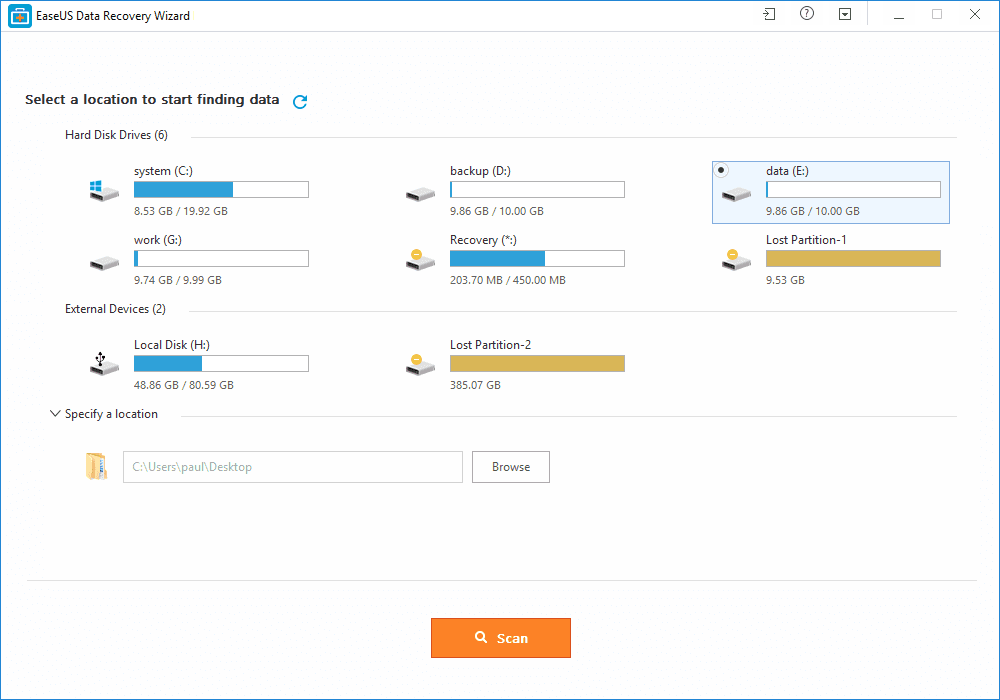
Step 1. First of all, you need to download and install EaseUS Data Recovery Wizard on your Windows computer and then launch it normally. You need to select the location where you want to scan and then click on 'Scan'
Step 2. Now, wait for few minutes until the tool finishes scanning your drive. The tool search for files that got deleted or cleaned from the Recycle Bin.
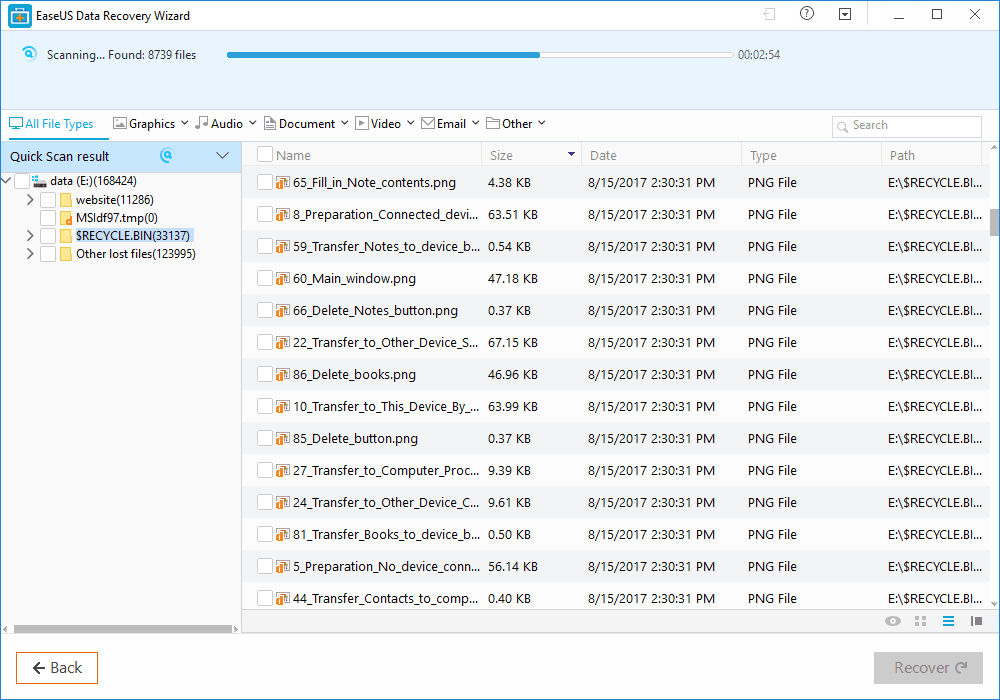
Step 3. Now it will show you files that you can recover. Here you need to click on the file which you want to recover and click on 'Recover'
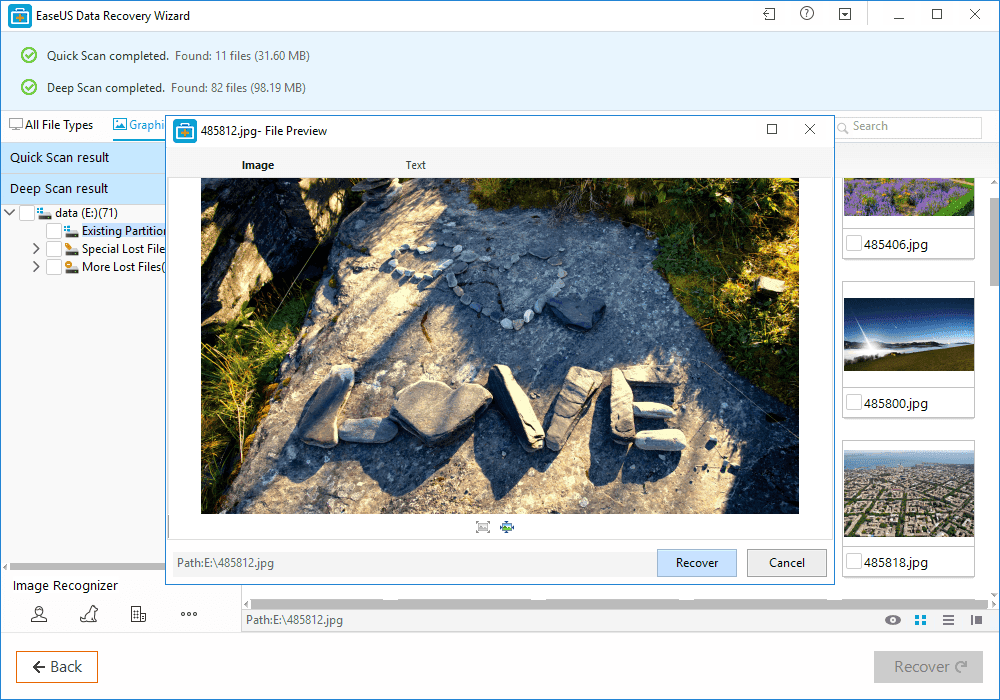
That's it, you are done! This is how you can use EaseUS data recovery to get back your deleted files on your computer.

Benefits of EaseUS Data Recovery

Well, the data recovery tool provided by EaseUS comes with many benefits. It can not only recover accidentally deleted files, but it can also recover data in case of Virus Attacks, Hard Disk Damage, OS Crash etc.
You can also use this awesome data recovery wizard to recover deleted files from External Disk, USB Drive, Camcorder, Mobile Devices, Zip Drive, iPod, Music Player and more.
Overall, this is one of the best data recovery tools you can have on your Windows computer. EaseUS Data Recovery also has a free version with restricted features. Overall, this is a stress-free solution to get back your deleted files
Related articles

Testing SAML Endpoints For XML Signature Wrapping Vulnerabilities

A lot can go wrong when validating SAML messages. When auditing SAML endpoints, it's important to look out for vulnerabilities in the signature validation logic. XML Signature Wrapping (XSW) against SAML is an attack where manipulated SAML message is submitted in an attempt to make the endpoint validate the signed parts of the message -- which were correctly validated -- while processing a different attacker-generated part of the message as a way to extract the authentication statements. Because the attacker can arbitrarily forge SAML assertions which are accepted as valid by the vulnerable endpoint, the impact can be severe. [1,2,3]

Testing for XSW vulnerabilities in SAML endpoints can be a tedious process, as the auditor needs to not only know the details of the various XSW techniques, but also must handle a multitude of repetitive copy-and-paste tasks and apply the appropriate encoding onto each message. The latest revision of the XSW-Attacker module in our BurpSuite extension EsPReSSo helps to make this testing process easier, and even comes with a semi-automated mode. Read on to learn more about the new release! 

 SAML XSW-Attacker

After a signed SAML message has been intercepted using the Burp Proxy and shown in EsPReSSO, you can open the XSW-Attacker by navigating to the SAML tab and then the Attacker tab.  Select Signature Wrapping from the drop down menu, as shown in the screenshot below:


To simplify its use, the XSW-Attacker performs the attack in a two step process of initialization and execution, as reflected by its two tabs Init Attack and Execute Attack. The interface of the XSW-Attacker is depicted below.
XSW-Attacker overview

The Init Attack tab displays the current SAML message. To execute a signature wrapping attack, a payload needs to be configured in a way that values of the originally signed message are replaced with values of the attacker's choice. To do this, enter the value of a text-node you wish to replace in the Current value text-field. Insert the replacement value in the text-field labeled New value and click the Add button. Multiple values can be provided; however, all of which must be child nodes of the signed element. Valid substitution pairs and the corresponding XPath selectors are displayed in the Modifications Table. To delete an entry from the table, select the entry and press `Del`, or use the right-click menu.

Next, click the Generate vectors button - this will prepare the payloads accordingly and brings the Execute Attack tab to the front of the screen.

At the top of the Execute Attack tab, select one of the pre-generated payloads. The structure of the selected vector is explained in a shorthand syntax in the text area below the selector.
The text-area labeled Attack vector is editable and can be used to manually fine-tune the chosen payload if necessary. The button Pretty print opens up a syntax-highlighted overview of the current vector.
To submit the manipulated SAML response, use Burp's Forward button (or Go, while in the Repeater).

Automating XSW-Attacker with Burp Intruder

Burp's Intruder tool allows the sending of automated requests with varying payloads to a test target and analyzes the responses. EsPReSSO now includes a Payload Generator called XSW Payloads to facilitate when testing the XML processing endpoints for XSW vulnerabilities. The following paragraphs explain how to use the automated XSW attacker with a SAML response.

First, open an intercepted request in Burp's Intruder (e.g., by pressing `Ctrl+i`). For the attack type, select Sniper. Open the Intruder's Positions tab, clear all payload positions but the value of the XML message (the `SAMLResponse` parameter, in our example). Note: the XSW-Attacker can only handle XML messages that contain exactly one XML Signature.
Next, switch to the Payloads tab and for the Payload Type, select Extension-generated. From the newly added Select generator drop-down menu, choose XSW Payloads, as depicted in the screenshot below.


While still in the Payloads tab, disable the URL-encoding checkbox in the Payload Encoding section, since Burp Intruder deals with the encoding automatically and should suffice for most cases.
Click the Start Attack button and a new window will pop up. This window is shown below and is similar to the XSW Attacker's Init Attack tab.


Configure the payload as explained in the section above. In addition, a schema analyzer can be selected and checkboxes at the bottom of the window allow the tester to choose a specific encoding. However, for most cases the detected presets should be correct.

Click the Start Attack button and the Intruder will start sending each of the pre-generated vectors to the configured endpoint. Note that this may result in a huge number of outgoing requests. To make it easier to recognize the successful Signature Wrapping attacks, it is recommended to use the Intruder's Grep-Match functionality. As an example, consider adding the replacement values from the Modifications Table as a Grep-Match rule in the Intruder's Options tab. By doing so, a successful attack vector will be marked with a checkmark in the results table, if the response includes any of the configure grep rules.

Credits

EsPReSSO's XSW Attacker is based on the WS-Attacker [4] library by Christian Mainka and the original adoption for EsPReSSO has been implemented by Tim Günther.
Our students Nurullah Erinola, Nils Engelberts and David Herring did a great job improving the execution of XSW and implementing a much better UI.

---

[1] On Breaking SAML - Be Whoever You Want to Be
[2] Your Software at My Service
[3] Se­cu­ri­ty Ana­ly­sis of XAdES Va­li­da­ti­on in the CEF Di­gi­tal Si­gna­tu­re Ser­vices (DSS)
[4] WS-Attacker

Related word


macSubstrate - Tool For Interprocess Code Injection On macOS


macSubstrate is a platform tool for interprocess code injection on macOS, with the similar function to Cydia Substrate on iOS. Using macSubstrate, you can inject your plugins (.bundle or .framework) into a mac app (including sandboxed apps) to tweak it in the runtime.
  • All you need is to get or create plugins for your target app.
  • No trouble with modification and codesign for the original target app.
  • No more work after the target app is updated.
  • Super easy to install or uninstall a plugin.
  • Loading plugins automatically whenever the target app is relaunched.
  • Providing a GUI app to make injection much easier.

Prepare
  • Disable SIP
  • Why should disable SIP
    System Integrity Protection is a new security policy that applies to every running process, including privileged code and code that runs out of the sandbox. The policy extends additional protections to components on disk and at run-time, only allowing system binaries to be modified by the system installer and software updates. Code injection and runtime attachments to system binaries are no longer permitted.

Usage
  1. download macSubstrate.app, put into /Applications and launch it.
    StatusBar
  2. grant authorization if needed.
  3. install a plugin by importing or dragging into macSubstrate.
    ToInstall
  4. launch the target app.
    step 3 and step 4 can be switched
    Once a plugin is installed by macSubstrate, it will take effect immediately. But if you want it to work whenever the target app is relaunched or macOS is restarted, you need to keep macSubstrate running and allow it to automatically launch at login.
  5. uninstall a plugin when you do not need it anymore.
    Installed

Plugin
macSubstrate supports plugins of .bundle or .framework, so you just need to create a valid .bundle or .framework file. The most important thing is to add a key macSubstratePlugin into the info.plist, with the dictionary value:
Key Value
TargetAppBundleID the target app's CFBundleIdentifier, this tells macSubstrate which app to inject.
Description brief description of the plugin
AuthorName author name of the plugin
AuthorEmail author email of the plugin
Please check the demo plugins demo.bundle and demo.framework for details.

Xcode Templates
macSubstrate also provides Xcode Templates to help you create plugins conveniently:
  1. ln -fhs ./macSubstratePluginTemplate ~/Library/Developer/Xcode/Templates/macSubstrate\ Plugin
  2. Launch Xcode, and there will be 2 new plugin templates for you.

Security
  1. SIP is a new security policy on macOS, which will help to keep you away from potential security risk. Disable it means you will lose the protection from SIP.
  2. If you install a plugin from a developer, you should be responsible for the security of the plugin. If you do not trust it, please do not install it. macSubstrate will help to verify the code signature of a plugin, and I suggest you to scan it using VirusTotal. Anyway, macSubstrate is just a tool, and it is your choice to decide what plugin to install.


Related articles

Evil Limiter: Taking Control Of Your Network Bandwidth


Ever wanted to block someone from the network or limit their bandwidth without having the network admin privileges? Well Evil Limiter has got you covered then.


An amazing tool to help you control your network without having access to the admin panel.

Today I'm gonna show you how to use this interesting tool to take control of your network.


Requirements:

1. A PC or Laptop with Linux OS.
2. A Network Adapter.
3. Access to the Network you want to control.
4. sudo or root access on your Linux OS.

First of all we will download the tool from its github repository:

https://github.com/bitbrute/evillimiter

You can download and extract the zip file from the link above or you can clone evillimiter repository using git like this:


git clone https://github.com/bitbrute/evillimiter 


Now lets install the downloaded tool on our machine

Step 1: Move inside the downloaded github repository

cd evillimiter


Step 2: To install type


sudo python3 setup.py install


wait for the installation to finish (May take some time)


Step 3: To run type


sudo evilimiter


Voila! That's it, you got it up and running on your machine


Now how do you control your network with it, its very easy.

It should detect your network automatically but yeah you can set it up manually as well using the command line argument -i.

After you have selected the right interface to control, you need to scan your network for live hosts. To perform the scan type


scan


you can pass an optional flag to the scan command which is range which will help you to specify the range of ip addresses you want to scan like this


scan --range 192.168.1.1-192.168.1.100


The above command will scan a total of 100 hosts from 192.168.1.1 to 192.168.1.100


Now after you have scanned your network next thing is to list the hosts that have been discovered during the scan for that you type the hosts command like this


hosts


Now you know the hosts on your network and now you should know which host you wanna block or limit based on the mac address of the host. Remember the host id of the host that you want to block or limit bandwidth of and lets do the magic.

to block a host from using the internet we simply specify the block command followed by the host id of the host that we want to block like this

block 1


if instead of blocking the host we just want to limit his internet bandwidth we can do just that by using the limit command followed by the host id and then the bandwidth that we want to allocate to that particular host like this


limit 1 100kbits


Wohooo! yeah its that easy and yes you can do all this without having the network admin role.

Now if you want to show mercy on that poor guy (blocked host), you can set him free by using the free command followed by the host id like this:

free 1


Well isn't administrating your network bandwidth so easy now.

Hope you enjoyed this tutorial.:)

More info

  1. Pentest Vs Ethical Hacking
  2. Hacking Site
  3. Hacking Groups
  4. Hacker News
  5. Pentest Partners
  6. Hacker Code
  7. Pentest Smtp
  8. Pentest Jobs
  9. Hacking Linux

segunda-feira, 8 de junho de 2020

DirBuster: Brute Force Web Directories


"DirBuster is a multi threaded java application designed to brute force directories and files names on web/application servers. Often is the case now of what looks like a web server in a state of default installation is actually not, and has pages and applications hidden within. DirBuster attempts to find these. However tools of this nature are often as only good as the directory and file list they come with. A different approach was taken to generating this. The list was generated from scratch, by crawling the Internet and collecting the directory and files that are actually used by developers! DirBuster comes a total of 9 different lists (Further information can be found below), this makes DirBuster extremely effective at finding those hidden files and directories. And if that was not enough DirBuster also has the option to perform a pure brute force, which leaves the hidden directories and files nowhere to hide! If you have the time ;) " read more...

Download: https://sourceforge.net/projects/dirbuster

Related news


Cain And Abel

"Cain & Abel is a password recovery tool for Microsoft Operating Systems. It allows easy recovery of various kind of passwords by sniffing the network, cracking encrypted passwords using Dictionary, Brute-Force and Cryptanalysis attacks, recording VoIP conversations, decoding scrambled passwords, recovering wireless network keys, revealing password boxes, uncovering cached passwords and analyzing routing protocols. The program does not exploit any software vulnerabilities or bugs that could not be fixed with little effort. It covers some security aspects/weakness present in protocol's standards, authentication methods and caching mechanisms; its main purpose is the simplified recovery of passwords and credentials from various sources, however it also ships some "non standard" utilities for Microsoft Windows users." read more...

Website: http://www.oxid.it/cain.html

Continue reading


  1. Pentest Bootcamp
  2. Pentest Azure
  3. Hacker Lab
  4. Hacking Youtube
  5. Pentest Ftp
  6. Hacking Games Online
  7. What Hacking Is
  8. Hacking
  9. Pentest Bootcamp
  10. Hacking Typer
  11. Hacking Attack
  12. Pentest Vs Ethical Hacking
  13. Hacking Box

Vlang Binary Debugging

Why vlang? V is a featured, productive, safe and confortable language highly compatible with c, that generates neat binaries with c-speed, the decompilation also seems quite clear as c code.
https://vlang.io/

After open the binary with radare in debug mode "-d" we proceed to do the binary recursive analysis with "aaaa" the more a's the more deep analys.


The function names are modified when the binary is crafted, if we have a function named hello in a module named main we will have the symbol main__hello, but we can locate them quicly thanks to radare's grep done with "~" token in this case applied to the "afl" command which lists all the symbols.


Being in debug mode we can use "d*" commands, for example "db" for breakpointing the function and then "dc" to start or continue execution.


Let's dissasemble the function with "pD" command, it also displays the function variables and arguments as well, note also the xref "call xref from main"


Let's take a look to the function arguments, radare detect's this three 64bits registers used on the function.


Actually the function parameter is rsi that contains a testing html to test the href extraction algorithm.


The string structure is quite simple and it's plenty of implemented methods.


With F8 we can step over the code as we were in ollydbg on linux.


Note the rip marker sliding into the code.


We can recognize the aray creations, and the s.index_after() function used to find substrings since a specific position.


If we take a look de dissasembly we sill see quite a few calls to tos3() functions.
Those functions are involved in string initialization, and implements safety checks.

  • tos(string, len)
  • tos2(byteptr)
  • tos3(charptr)

In this case I have a crash in my V code and I want to know what is crashing, just continue the execution with "dc" and see what poits the rip register.


In visual mode "V" we can see previous instructions to figure out the arguments and state.


We've located the crash on the substring operation which is something like "s2 := s1[a..b]" probably one of the arguments of the substring is out of bounds but luckily the V language has safety checks and is a controlled termination:


Switching the basic block view "space" we can see the execution flow, in this case we know the loops and branches because we have the code but this view also we can see the tos3 parameter "href=" which is useful to locate the position on the code.


When it reach the substr, we can see the parameters with "tab" command.


Looking the implementation the radare parameter calculation is quite exact.


Let's check the param values:


so the indexes are from 0x0e to 0x24 which are inside the buffer, lets continue to next iteration,
if we set a breakpoint and check every iteration, on latest iteration before the crash we have the values 0x2c to 0x70 with overflows the buffer and produces a controlled termination of the v compiled process.


Read more


  1. Hacker Language
  2. Pentest Linux
  3. Hacking Wifi
  4. Hacking Box
  5. Hacker Keyboard
  6. Pentest Uk
  7. Pentest Windows 7
  8. Pentest Windows 7
  9. Hacking Ethics
  10. Pentest Tools Framework
  11. Pentest Documentation
  12. Pentest Wifi
  13. Pentest With Kali
  14. Pentest Kit
  15. Hacking Language
  16. Pentest Devices
  17. Pentest Wiki
  18. Hacking Process
  19. Hacking Hardware
  20. Pentest Tools Github